The Agent DMZ: How to Let AI Use Tools Without Giving It the Keys – Cloudflare Triple-T
AI agents are quickly moving from chat interfaces into operational workflows: opening tickets, querying logs, calling APIs, reading documents, and taking action through tools like MCP servers. That creates a new enterprise risk pattern: the model is not the only thing to secure—the tool path is now part of the network and identity control plane.
In this 10-minute Triple-T session, Aaron McAllister will share a practical “Agent DMZ” reference pattern that network and security teams can apply immediately. Attendees will learn how to separate agent access from human access, broker tool calls through least-privilege gateways, inspect prompts and responses for sensitive data, apply policy by actor/tool/data class, and preserve audit trails for every agent action.
The session will close with a five-control checklist teams can use to assess whether their first AI agent workflow is safe enough for production: identity, tool scoping, data boundaries, runtime inspection, and replayable observability.
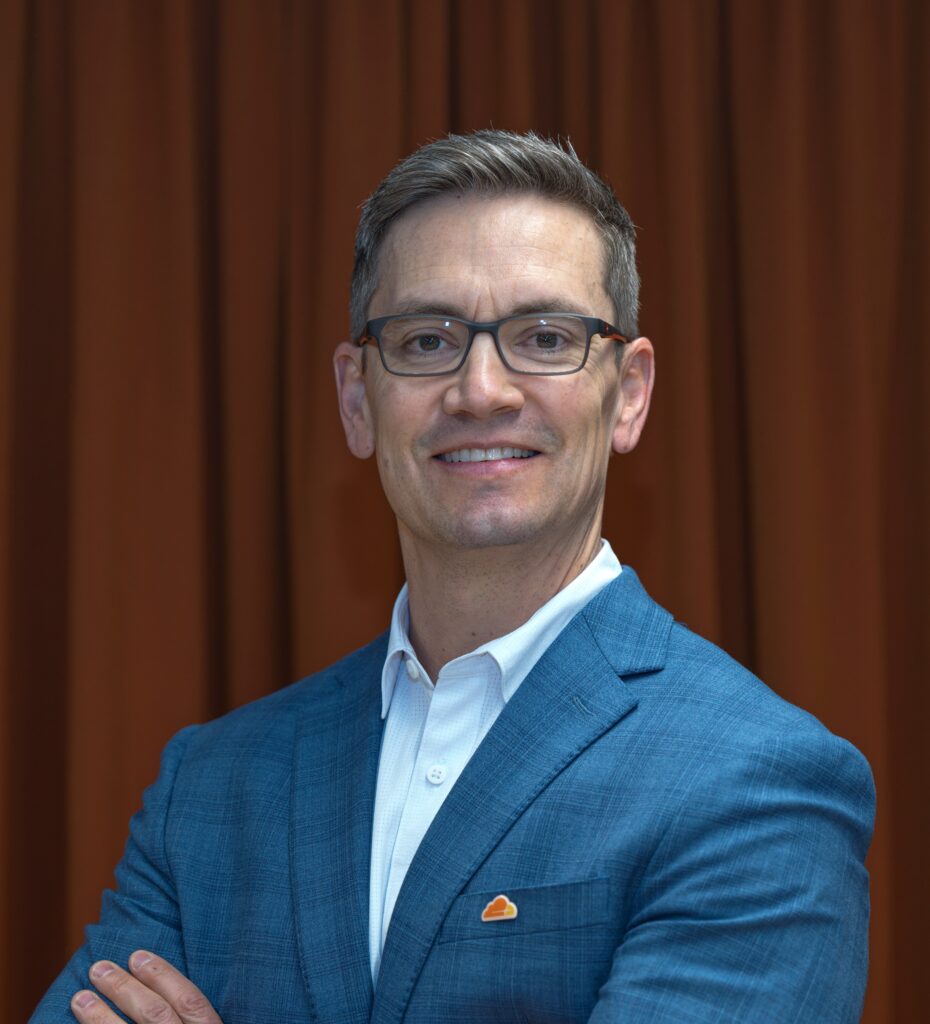
As a Field CTO at Cloudflare, Aaron McAllister helps the world’s leading organizations stay fast, secure, and resilient. With more than 25 years of real-world experience in cybersecurity and SASE, Aaron is known for his ability to distill complex technical hurdles into clear strategic advantages. Based in Denver, he is a frequent speaker and trusted advisor who moves beyond the “what” of technology to focus on the “why” for the modern digital landscape.